Trust & Security
Built by ISO auditors for audit success
When prospects or auditors ask about your security, you need demonstrable controls, not good intentions. Built by certified ISO 27001 Lead Auditors who know what passes audits—so you get security that works, not just checkboxes.
Demonstrate Data Protection
Enterprise-grade encryption (TLS 1.3, AES-256). Clear answers for auditors, not hand-waving.
Control Who Sees What
Role-based access control with audit trails. Demonstrate least-privilege principles to auditors with proof.
Answer Availability Questions
Daily backups, 30-day retention, 99.9% SLA. SOC 2 infrastructure you can reference.
Pass Audits Faster
Built by ISO 27001 auditors. GDPR, SOC 2, ISO 27001-aligned controls already meet expectations.
Data Privacy
Where is my data stored?
SOC 2 Type II certified data centers with enterprise-grade security. Point customers to documentation showing encryption and compliance.
Who has access to my data?
Only authorized team members. Support requires permission. Show auditors role-based controls and audit logs.
How is data backed up?
Daily backups, 30-day retention, point-in-time recovery. Documented procedures, not theoretical plans.
Compliance & Certifications
- GDPR Compliant: Consent tracking, data rights workflows, breach notification. Full EU compliance.
- SOC 2 Type II (In Progress): Infrastructure meeting enterprise security standards. Currently undergoing certification.
- ISO 27001 Aligned: Designed by certified auditors. Controls aligned with global security standards.
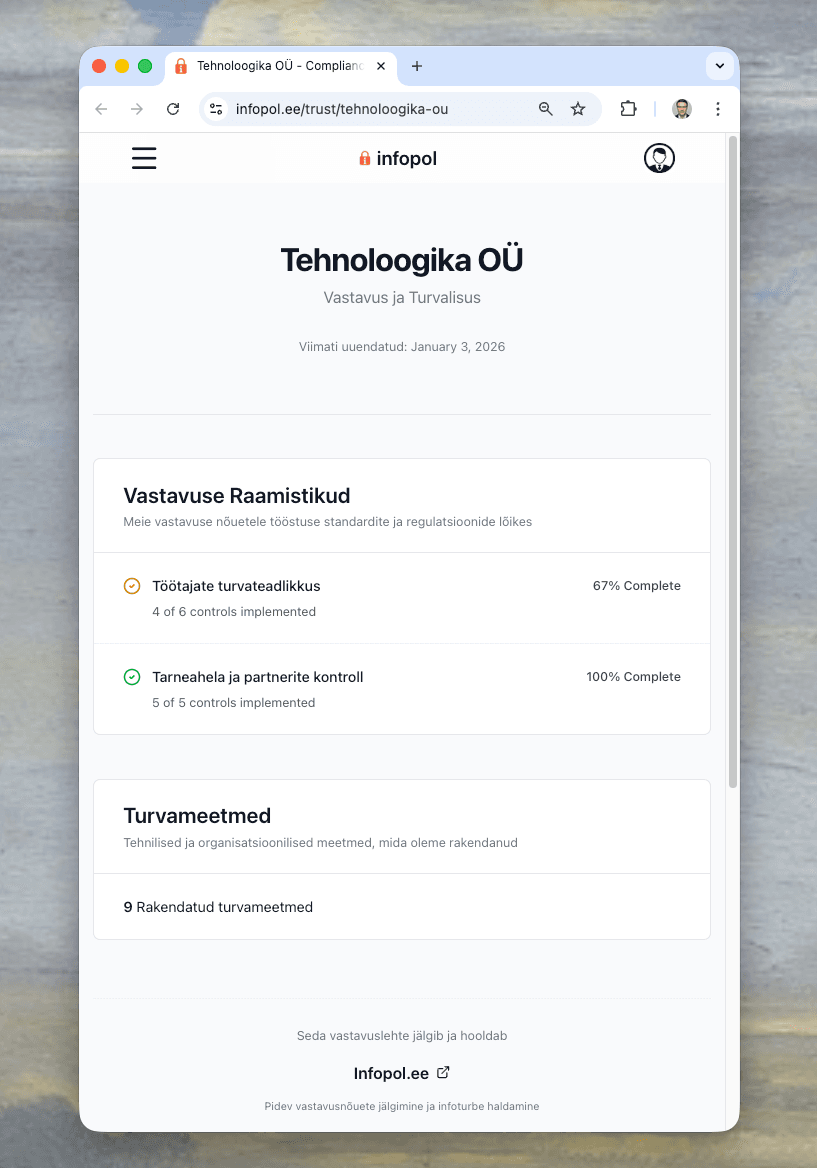
Your Public Trust Page
When enterprise buyers ask for compliance proof, send them a link. Your public page gives vendors and auditors instant visibility into your security.
- Replace questionnaires with your compliance URL
- Show compliance proof instantly to buyers
- Transparency projects confidence, not fear
- Control what frameworks and policies display
Screenshot example
Legal Documents
Professional legal documents ready when prospects request security documentation:
GDPR compliance and transparency
Security responsibilities and commitments
Tracking and consent management
Have Security Questions?
Questions about vendor security or audit requirements? Our certified ISO 27001 Lead Auditor explains how we help you meet compliance goals.
Audit-ready or your money back.
Talk to a Certified Auditor