We keep your E‑ITS 2026 information security system running
- we take responsibility for E-ITS compliance
- we prepare the documents and train your employees
- we provide monitoring and incident management
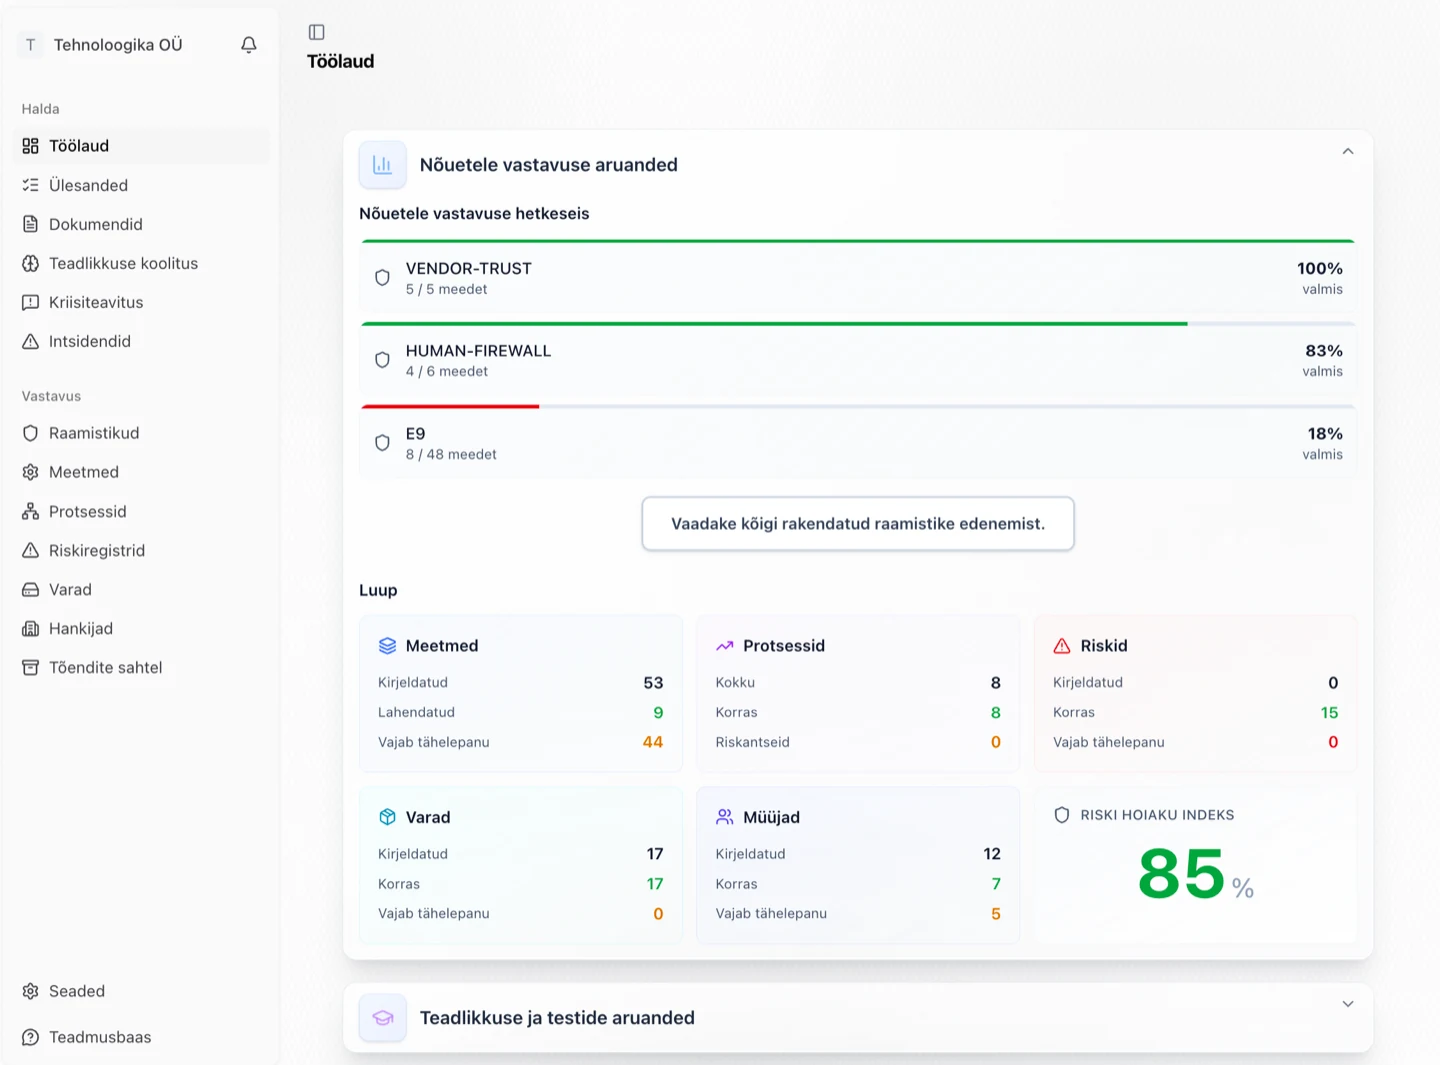
Everything the auditor needs is available and up to date.
We agree the scope of work and price before we start. Required training and document updates are included.
How Infopol improves day-to-day work.
Three short overviews. Each takes less than a minute.
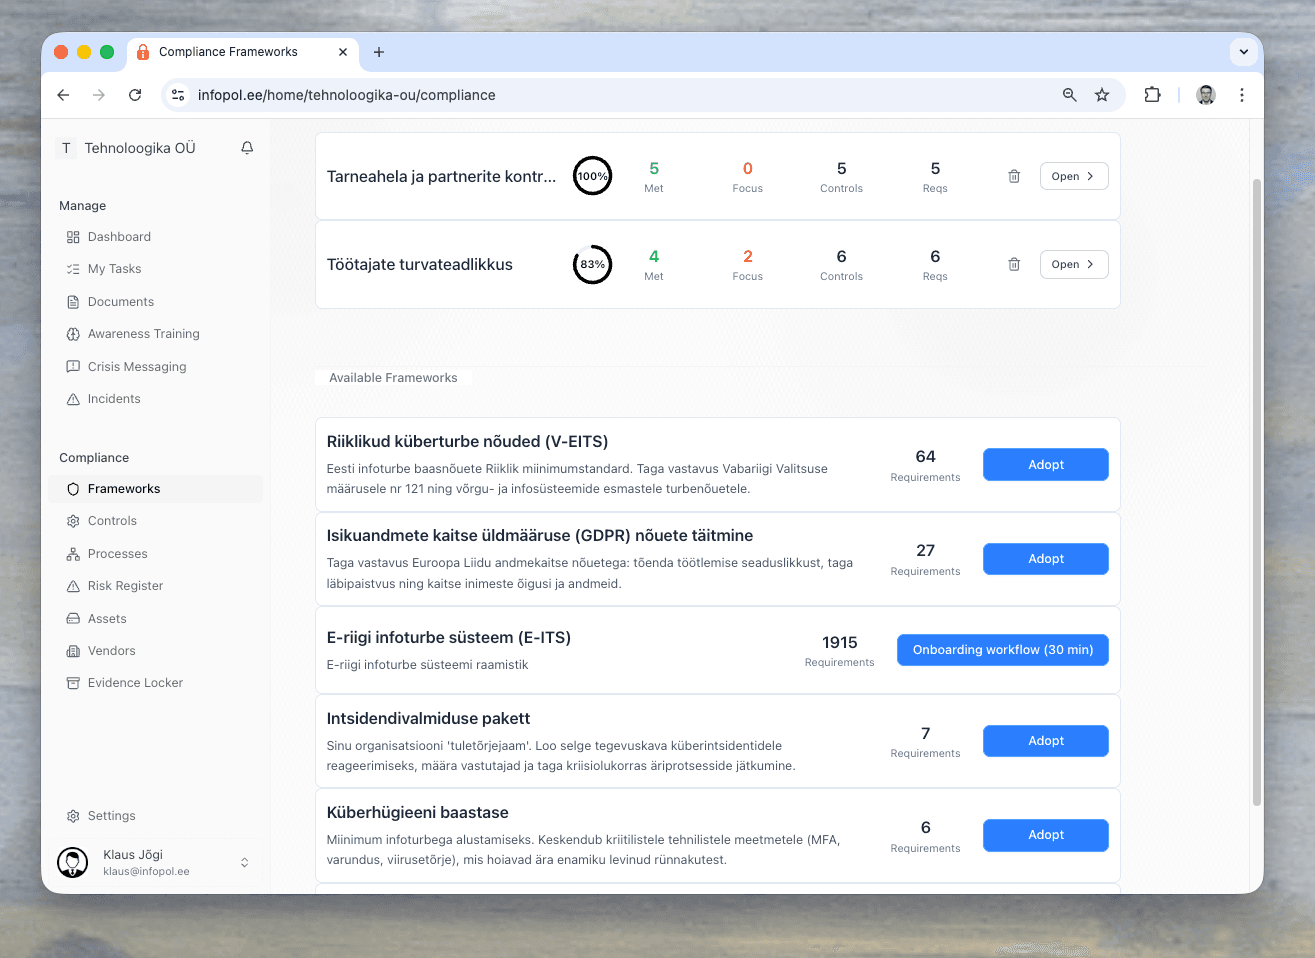
Choose a framework and get a clear action plan.
Choose ISO 27001, E-ITS, or NIS2. See immediately which requirements are met and which still need work. Every action has an owner and a deadline.
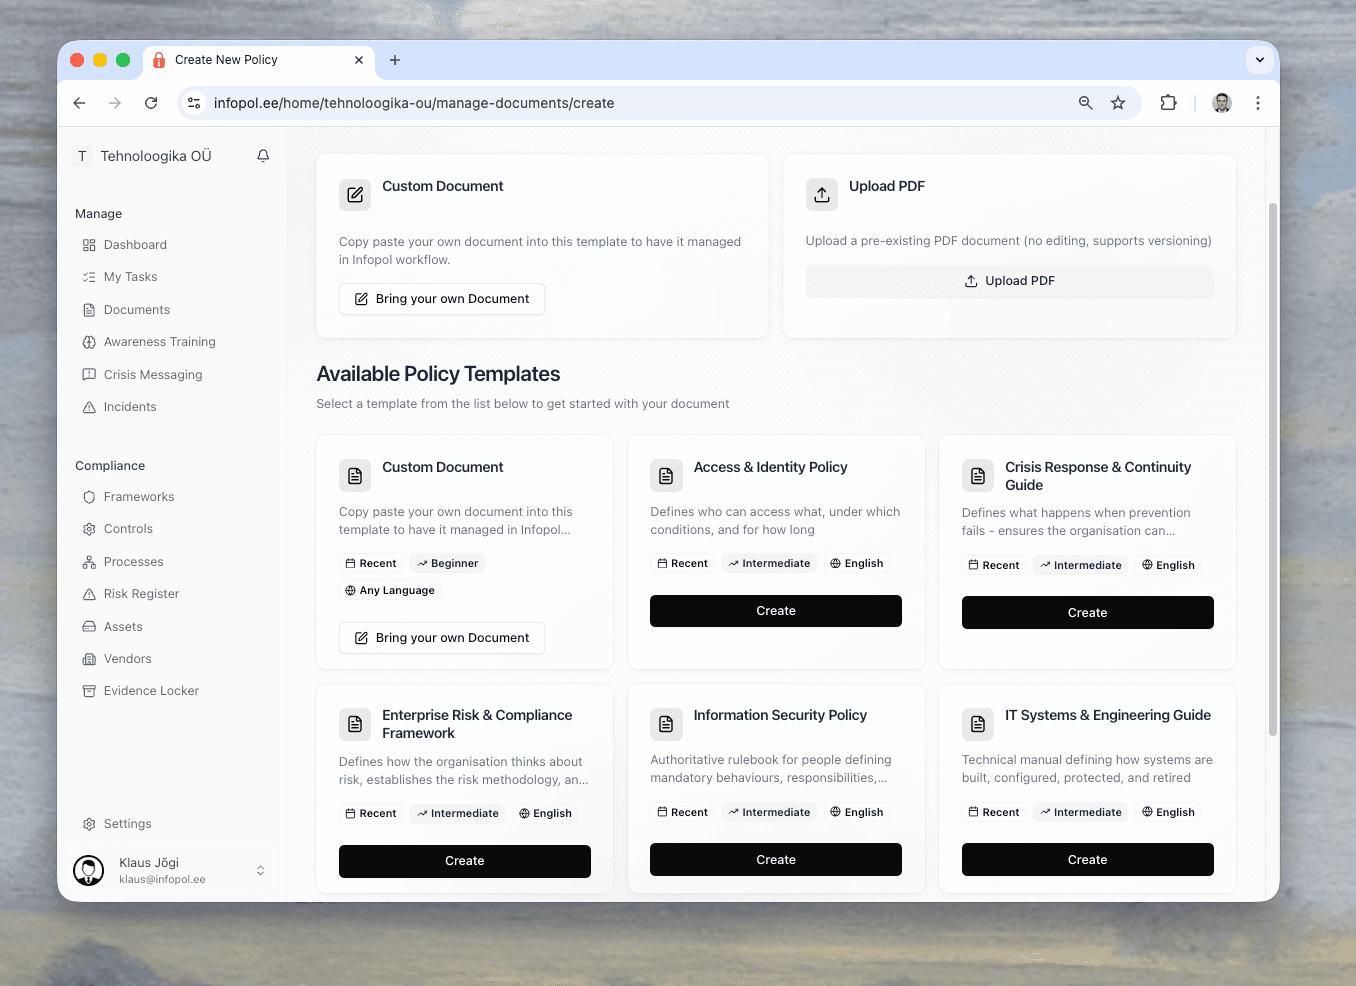
Policies, acknowledgements, and training in one system.
Send policies to employees, collect acknowledgements, and keep training records. All the evidence you need is added to the register automatically.
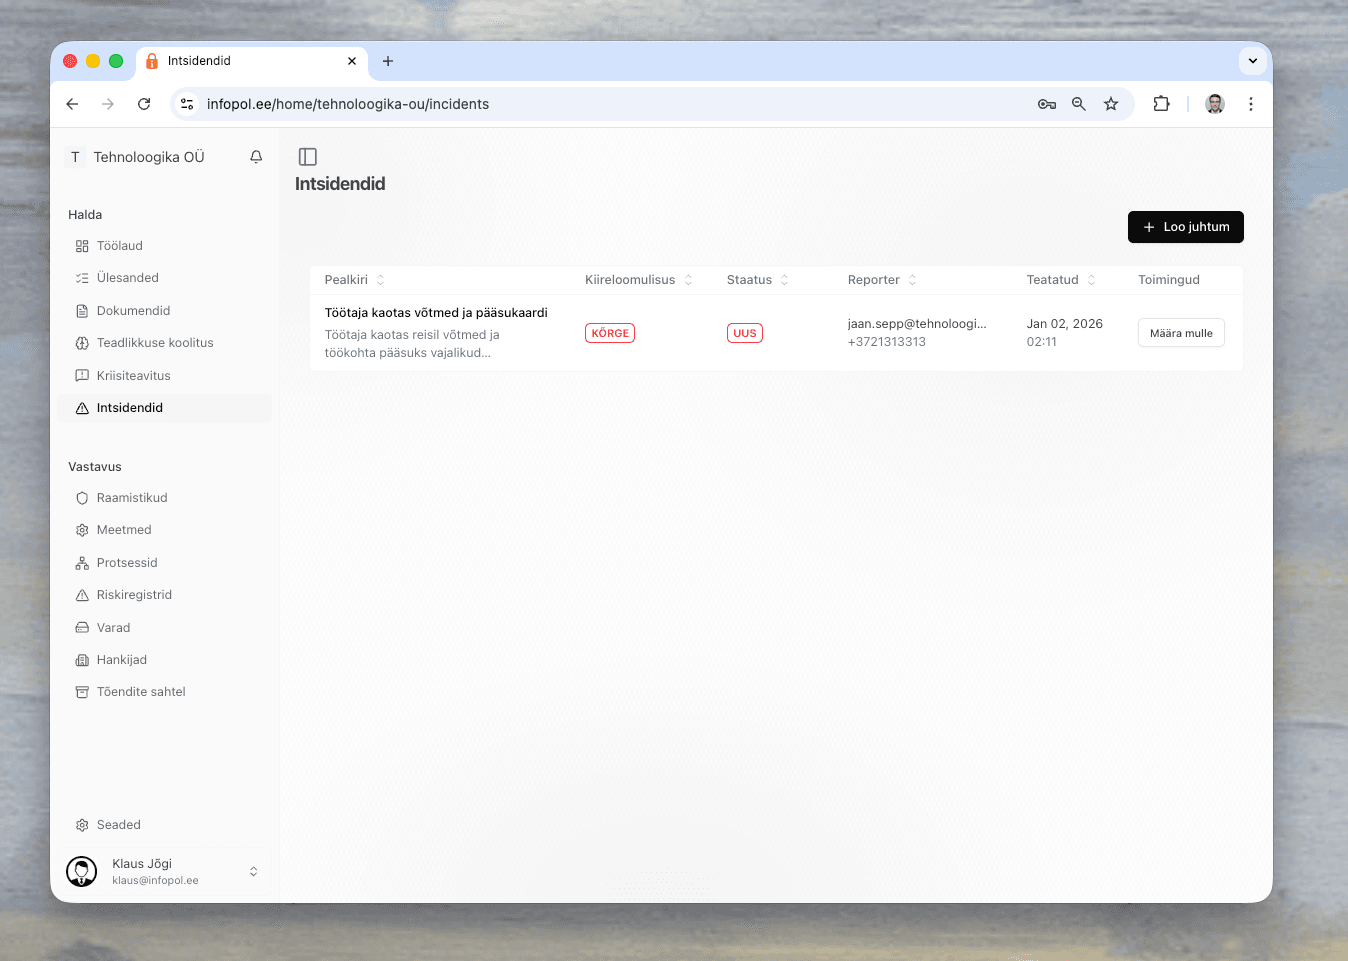
The next steps are clear when an incident occurs.
Log the incident, follow the action plan, and meet the reporting deadlines. The required register updates automatically as the work progresses.
How Infopol makes a customer's day-to-day work easier.
Clear advice, the work delivered on time, and everything documented the way an auditor expects. Easy people to deal with. We always knew where we stood.
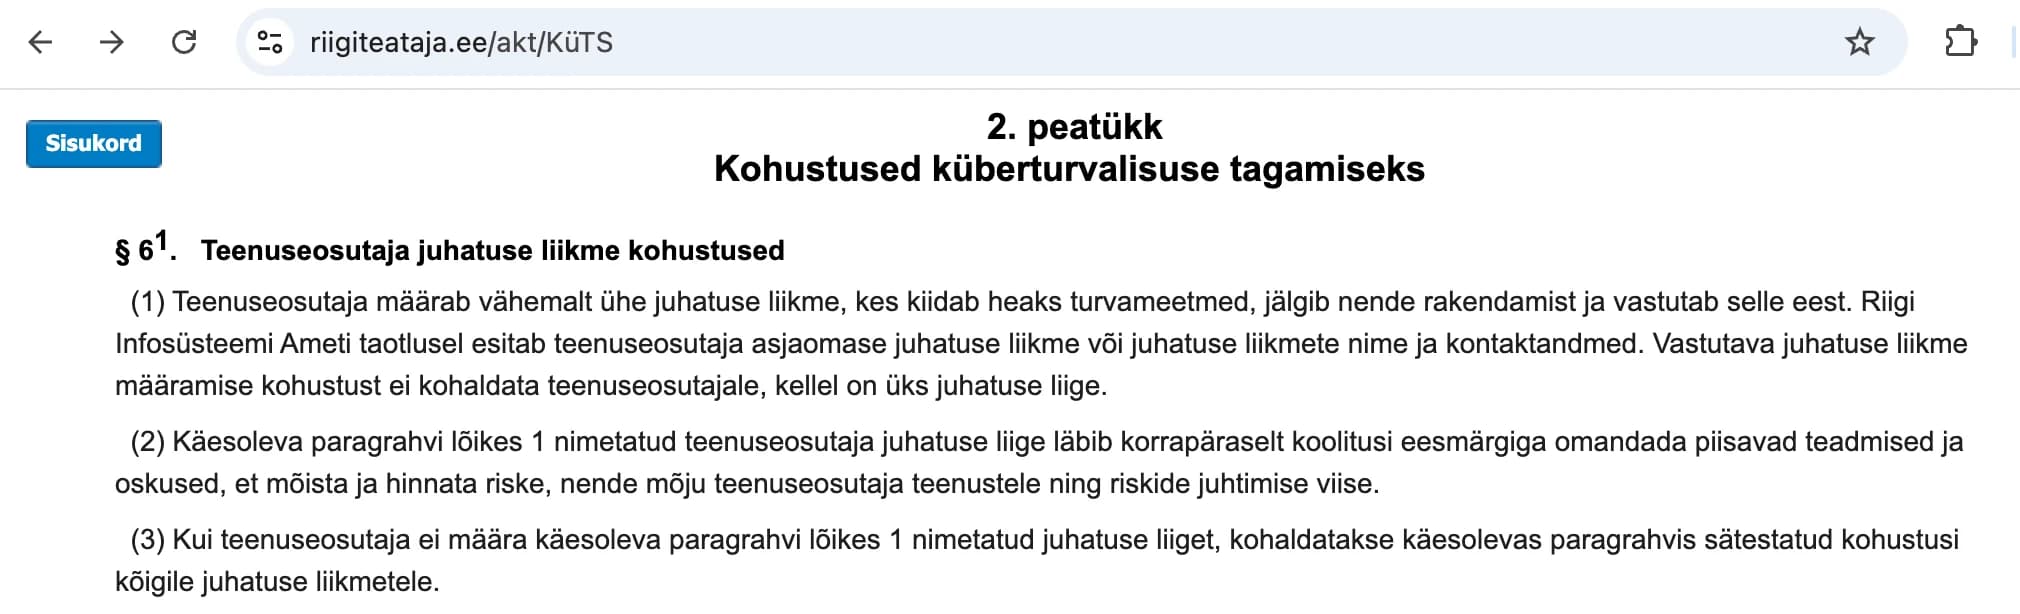
Organising information security is the company's responsibility.
A company within the scope of the Cybersecurity Act is responsible for organising the security of its systems and implementing the necessary measures. Compliance is easier to demonstrate when activities, documents, and responsibilities are kept consistently up to date.
If you are unsure whether the requirements apply to your company, ask us. The initial assessment is free.
Clear and straightforward answers.
Get a clear action plan and a fixed price.
Tell us briefly about your situation. We will review the work required and provide a written proposal with a timeline and guarantee terms. If Infopol is not the right partner for you, we will say so honestly.